
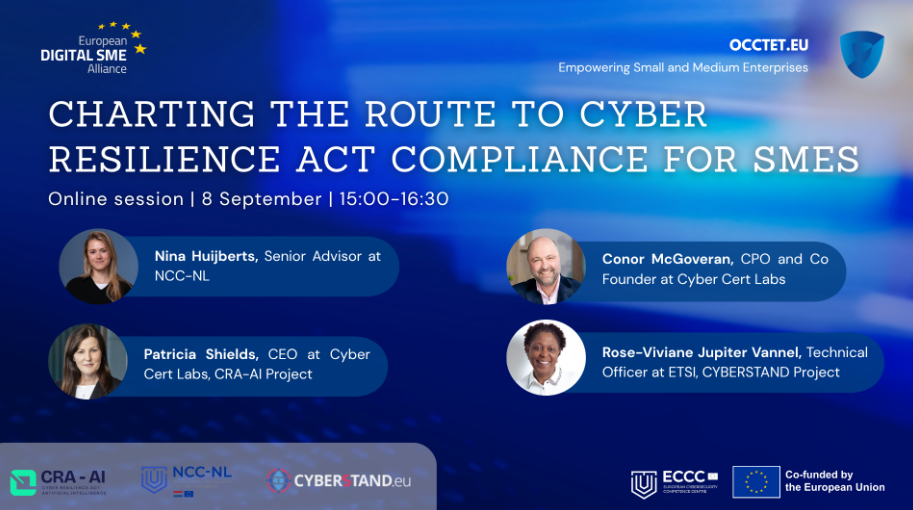
The Cyber Resilience Act (CRA) introduces horizontal cybersecurity requirements for products with digital elements placed on the EU market. Its main obligations apply from 11 December 2027, but the first major deadline arrives much sooner: from 11 September 2026, manufacturers must report actively exploited vulnerabilities and severe incidents affecting the security of product with digital elements to ENISA and national Computer Security Incident Response Teams. This webinar takes place three days before that date.
For many SMEs and micro-enterprises the CRA is both a new obligation and an unfamiliar one. With the first reporting obligations about to take effect, SMEs need practical guidance not only on what the CRA requires, but also on what they should be doing now and where they can find support.
This webinar is designed to provide exactly that orientation. In a single 90-minute session, it brings together the actors and the initiatives that can help SMEs navigate the CRA in practice.
This session will explore how NCC-NL, the National Coordination Centre for Cybersecurity in the Netherlands — the Dutch node in the European network of National Coordination Centres set up under the European Cybersecurity Competence Centre framework, supports SMEs in strengthening their cybersecurity and preparing for the Cyber Resilience Act. It will also cover NCC-NL’s role in the Dutch and European ecosystem, available funding opportunities under the Digital Europe Programme, and practical examples of EU-funded cybersecurity solutions. Participants will gain insights into how to access the support, funding and tools that can help their organisation become CRA-ready and strengthen its overall cyber resilience.
The webinar then presents two concrete pathways to compliance through the OCCTET and CRA-AI projects, each demonstrating its tools and outputs. Finally, the discussion will turn to the standardisation landscape and the case for a coordinated cluster on SME-facing CRA support.
Cyberstand.eu at the event
CYBERSTAND is represented by Rose-Viviane Jupiter Vannel, Technical Officer at ETSI.
She will join the session "Why harmonised standards matter for SMEs and how to engage with them", which addresses the role of harmonised standards in CRA compliance and how SMEs can engage early in the standardisation process.
The intervention leads into the closing discussion on building a coordinated cluster of SME-facing CRA support initiatives.